StyleSmuggler: The Magento Zero-Day Being Exploited Right Now
Sansec found an unpatched Magento and Adobe Commerce RCE under active attack since September 4, 2026. Here's how it works, what's affected, and what to check today.
PCI compliance guides, Magecart threat intelligence, and practical security advice for ecommerce merchants.
Sansec found an unpatched Magento and Adobe Commerce RCE under active attack since September 4, 2026. Here's how it works, what's affected, and what to check today.
What a CIPA demand letter is, what California's wiretapping law actually says, why many of these claims are weaker than they look, and what to do first.
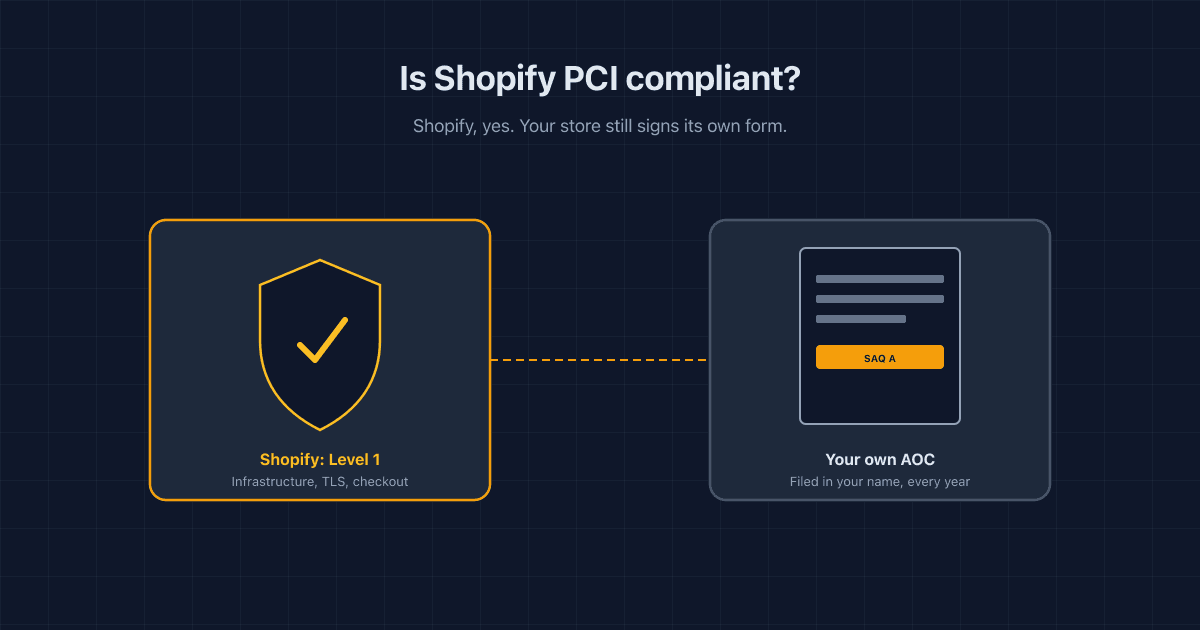
Shopify holds its own PCI Level 1 status, but that doesn't cover your store. Here's what Shopify handles, which SAQ you need, and what's still on you.
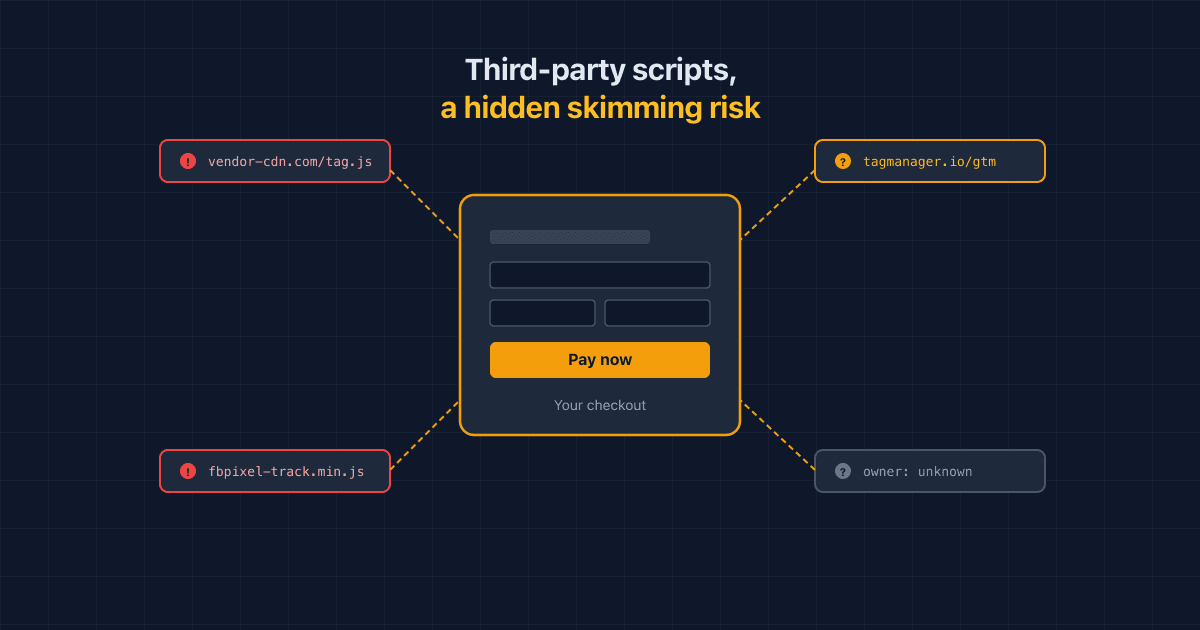
Sucuri warns that ordinary third-party scripts and tags can turn into a skimming risk on checkout pages. Here's how, and what PCI DSS 6.4.3/11.6.1 ask you to do.
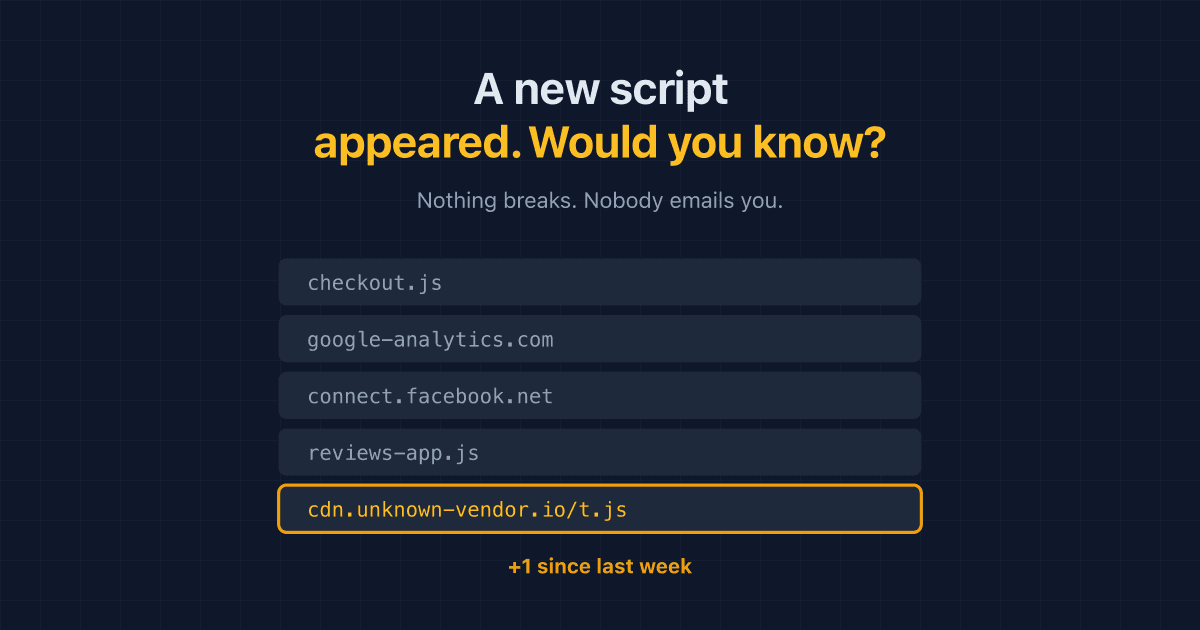
Third-party scripts arrive on ecommerce stores through app updates, theme edits and agency deploys, with no alert. What drift is, how to detect website changes, and what matters.
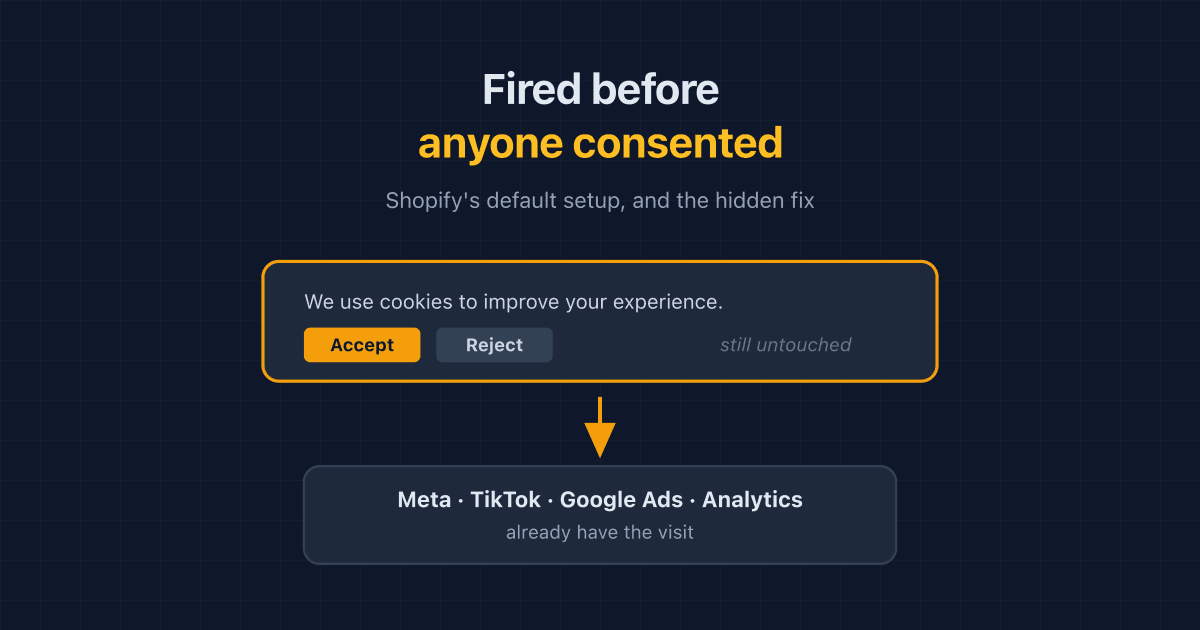
Shopify app pixels and custom pixels send data before a shopper answers your cookie banner, even when permissions look required. How to check, and the hidden fix.
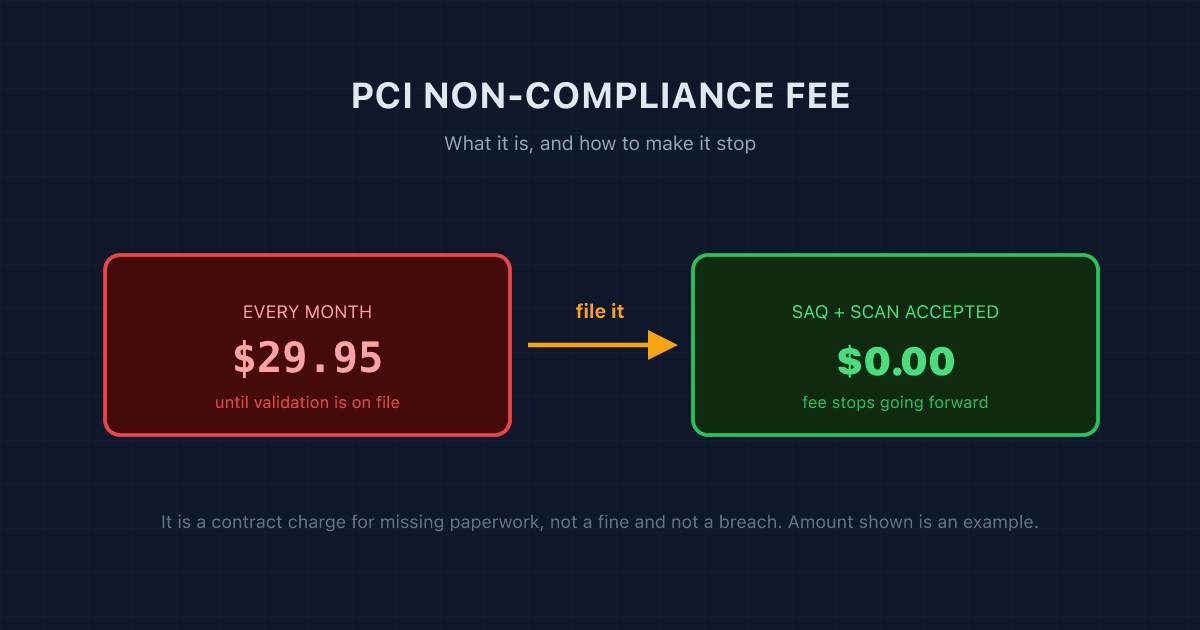
A PCI non-compliance fee is a monthly charge for missing validation paperwork, not a fine. Here is what triggers it, what it costs, and the five steps that stop it.
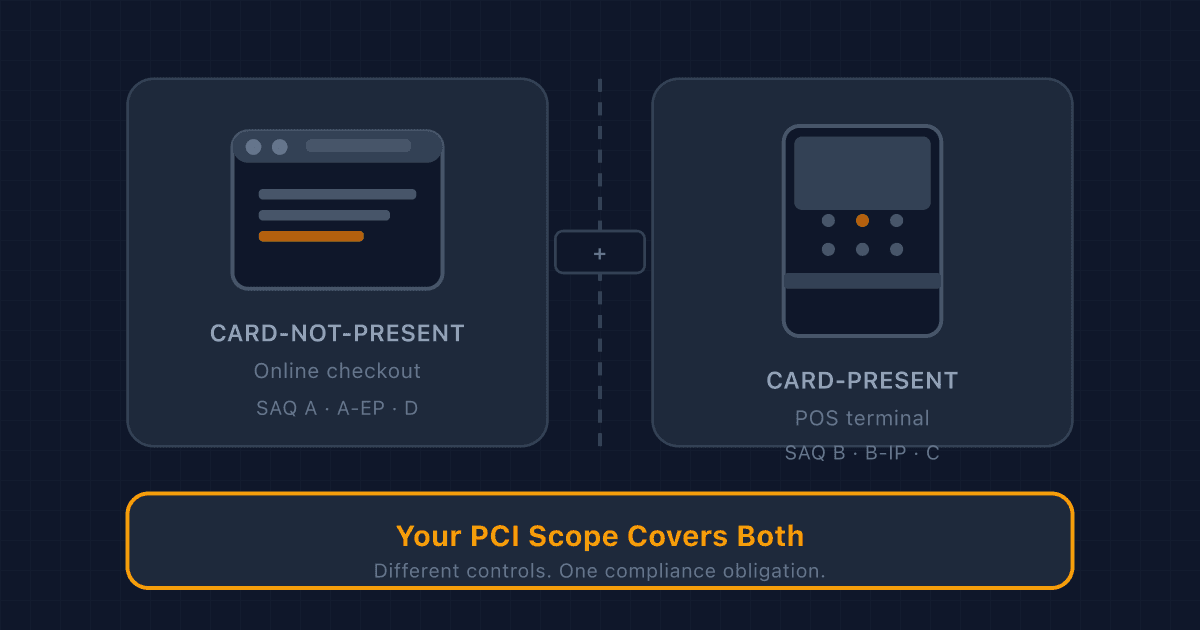
Card-present and card-not-present transactions fall under different PCI rules. If you sell both online and in person, here's what changes: SAQ type, network segmentation, physical device inspection, and who handles what.
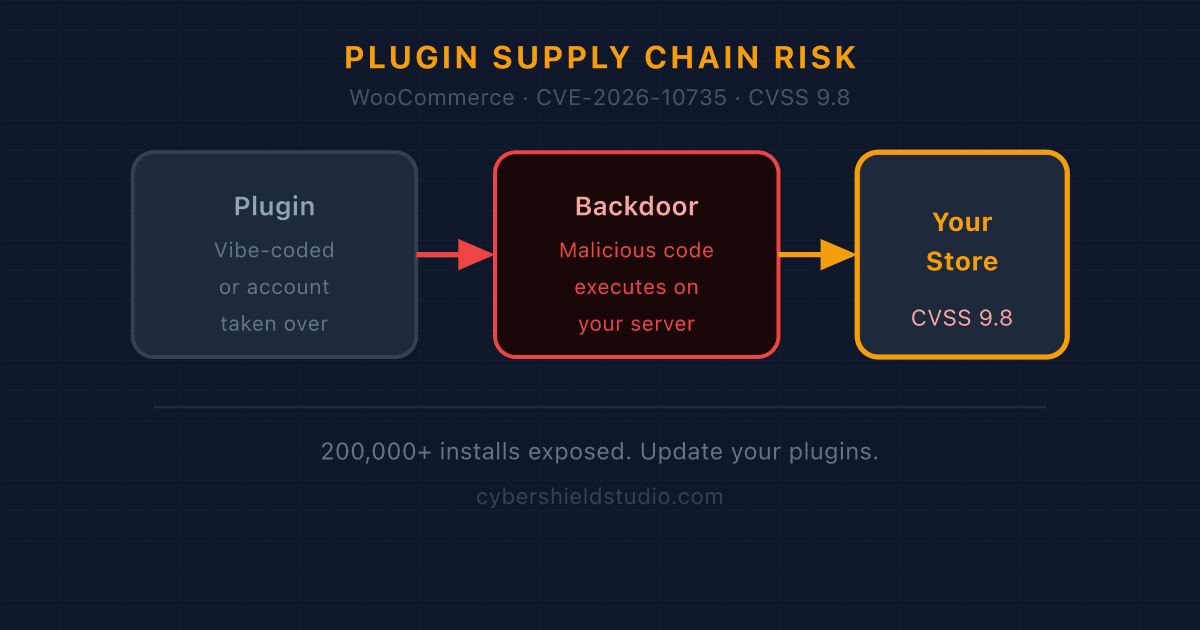
A CVSS 9.8 backdoor in a plugin with 200,000+ installs showed what happens when AI-generated code ships without security review. Here's what WooCommerce store owners need to know.
PCI compliance guides and ecommerce threat intelligence, straight to your inbox.
No spam, unsubscribe anytime. We handle your address as described in our privacy policy.